

Choosing managed IT services in Costa Mesa and nearby Tustin means evaluating how well a provider prevents problems before they reach your team. The right partner replaces emergency break-fix calls with continuous monitoring, documented security practices, and recovery plans that keep your business running through outages or cyber incidents.
See how we deliver managed IT services in Tustin, and our managed IT services in Costa Mesa.
This guide breaks down the capabilities that matter most for Tustin businesses, from local response readiness to compliance support for healthcare and professional services firms.
Key Takeaways
- Providers with physical offices in your area can reach your site faster when hardware fails or security incidents require hands-on response.
- Managed IT should include proactive monitoring and maintenance, not just help desk tickets when systems break.
- Cybersecurity must be built into the core service, covering endpoints, email, and incident response rather than treated as an optional add-on.
- Documented backup and recovery capabilities separate qualified providers from those who merely install backup software without testing restoration.
Local Presence and On-Site Readiness for Tustin Businesses
A provider’s physical proximity to your office directly affects how quickly they can resolve issues that demand hands-on attention. Server hardware failures, network equipment replacements, and security incident remediation all move faster when a technician can arrive within minutes rather than hours.
Tustin sits at the center of Orange County’s business corridor, surrounded by Costa Mesa, Santa Ana, Irvine, and other commercial hubs. Many businesses here operate across multiple locations, so a provider with local engineers who know the area’s infrastructure and traffic patterns can coordinate multi-site support more efficiently.
When evaluating providers, ask whether they maintain offices or dispatch facilities within Orange County and whether their service level agreements specify travel-time commitments. A provider who knows your building, your internet service options, and your local power grid can diagnose problems faster than one learning your environment from scratch.

Core Managed IT Coverage Beyond Break-Fix Support
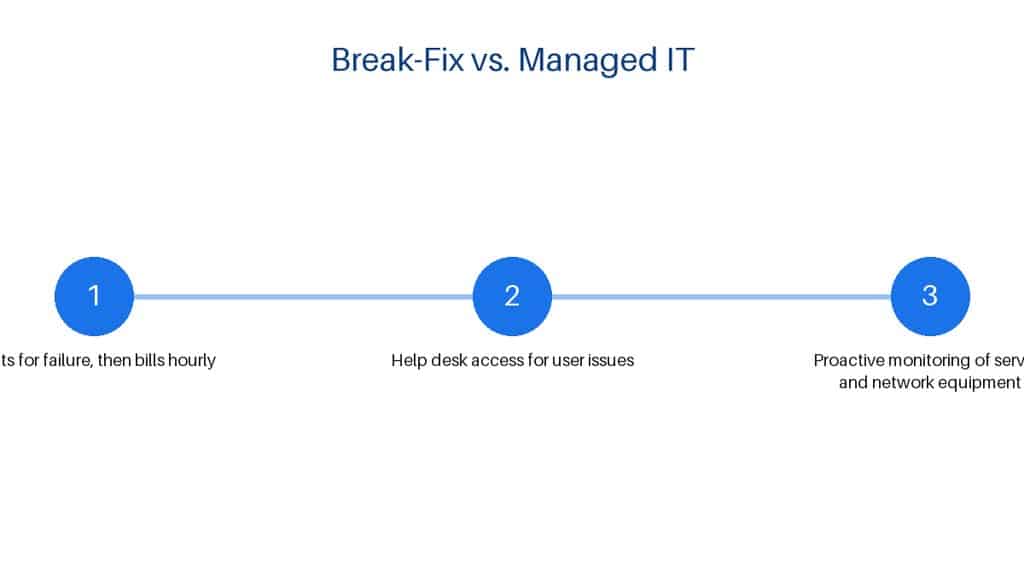
Break-fix support waits for failure, then bills hourly to resolve it. Managed IT services invert that model by monitoring systems continuously, applying patches on schedule, and addressing warning signs before they become outages.
A qualified provider should deliver ongoing operational support that includes help desk access for user issues, proactive monitoring of servers and network equipment, and infrastructure planning that aligns technology with business growth. This coverage turns IT from a reactive cost center into a stable, predictable operating expense.
The shift matters particularly for Tustin businesses with lean internal teams. A 20-person professional services firm cannot afford a full-time IT director, but it still needs the same reliability and security that larger enterprises demand.
Managed services bridge that gap with fractional expertise delivered as a flat-rate monthly plan.
Cybersecurity as a Built-In Service, Not an Add-On
Cybersecurity belongs inside the managed IT agreement, not sold separately as an upsell. Endpoint protection, ransomware and malware defense, email security filtering, and continuous security monitoring should be standard components that every client receives.
The threat landscape for small and mid-size businesses has intensified as attackers automate campaigns that indiscriminately target organizations with fewer defensive resources. A provider who treats security as optional leaves clients exposed to business-crippling incidents that could have been prevented.
Evaluate whether a prospective provider can articulate their security stack in plain language and demonstrate how it protects each layer of your environment. They should explain how endpoint agents detect anomalous behavior, how email filters block phishing and malicious attachments, and how their security operations center or monitoring platform responds to alerts outside business hours.
Backup, Recovery, and Business Continuity Documentation
Backup software is easy to install. Proven recovery capability is much harder to demonstrate, and that distinction separates competent providers from the rest.
A qualified managed IT partner should show you documented recovery procedures, tested restoration timelines, and a business continuity plan that accounts for your specific operational requirements.
Ask potential providers how often they test full system restores, what their recovery time objective is for critical systems, and whether they maintain offline or immutable copies that survive ransomware encryption of primary backups. These details reveal whether their backup strategy is a genuine safety net or merely a checkbox.
Business continuity planning extends beyond technology to include communication protocols, alternative workspace arrangements, and vendor coordination during extended outages. Tustin businesses near major transportation corridors face distinct risk profiles from construction, accidents, or regional power events, so continuity plans should address local scenarios.

Compliance Support for Healthcare and Regulated Industries
Tustin and surrounding Orange County communities host numerous medical practices, dental offices, and healthcare-related businesses subject to HIPAA requirements. These organizations need managed IT partners who understand that compliance is not a product you buy but a set of documented controls you maintain.
HIPAA technical safeguards require specific implementations around access controls, audit controls, integrity controls, and transmission security. A provider should be able to explain how their services map to each safeguard category and produce documentation that supports your compliance audits or breach investigations.
Even businesses outside healthcare benefit from this discipline. The security practices and documentation habits that satisfy HIPAA requirements, such as regular risk assessments and controlled access to sensitive data, strengthen defenses for any organization handling client or employee information.
Security Assessments and Proactive Vulnerability Management
A strong managed IT provider does not wait for attackers to find your weaknesses. They conduct security risk assessments, perform regular audits, manage vulnerability patching, and maintain incident response plans that define exactly who does what when a breach occurs.
This proactive posture matters because the median dwell time for attackers inside compromised networks often stretches for weeks or months before detection. Continuous assessment and rapid patching of discovered vulnerabilities shrinks that window and raises the cost and complexity for attackers.
When interviewing providers, ask for specifics about their assessment frequency, how they prioritize vulnerabilities for remediation, and whether they include incident response planning as a standard service component. Their answers will tell you whether they operate as a strategic security partner or a basic technology maintenance shop.

How GTI 24/7 Delivers Managed IT Services for Tustin and Orange County
GTI 24/7 was established in 2004 and offers custom IT solutions for small and medium-sized businesses, healthcare organizations, and enterprises throughout Orange County. The company combines services to provide customized help and guidance so clients receive only what they need rather than rigid packaged solutions.
GTI 24/7 provides proactive monitoring and maintenance that identifies and resolves issues before they interrupt operations, replacing break-fix repairs with managed IT services designed for stability. Clients can scale technology with their business through flexible IT services that support new tools, cloud adoption, and expanding teams.
The company offers remote support to handle tech issues quickly without requiring on-site visits, described by clients as making everything easy.
Frequently Asked Questions
What should Tustin businesses prioritize when comparing managed IT services in Costa Mesa and nearby areas?
Prioritize providers who include proactive monitoring, documented security practices, and tested recovery capabilities as standard offerings rather than upgrades. Local presence matters for rapid on-site response, but the quality of remote support and prevention is equally important.
How does managed IT differ from break-fix support for a small business?
Break-fix support responds to failures after they occur and bills by the hour. Managed IT services monitor systems continuously, apply preventive maintenance, and charge a flat monthly rate that covers both prevention and response.
The result is fewer outages and predictable budgeting.
Why should cybersecurity be included in core managed IT rather than purchased separately?
Modern threats target small and mid-size businesses with automated campaigns that do not discriminate by industry. Separating security from IT management creates gaps in coverage, delays in response, and confusion about responsibility when incidents occur.
Integrated security ensures every client receives baseline protection.
What compliance capabilities should healthcare businesses in Tustin expect from a managed IT provider?
Healthcare businesses should expect providers who can support HIPAA technical safeguards through documented access controls, audit logging, encryption, and risk assessment processes. The provider should explain how their services map to specific safeguard requirements and produce documentation for compliance audits.
How can a business evaluate whether a provider’s backup and recovery claims are legitimate?
Ask for specific recovery time objectives, how often full restoration tests occur, and whether offline or immutable backup copies exist. Legitimate providers welcome these questions and can demonstrate tested procedures rather than simply listing software features.
